Why Hardware Visibility Is Becoming Critical for Modern IT Infrastructure
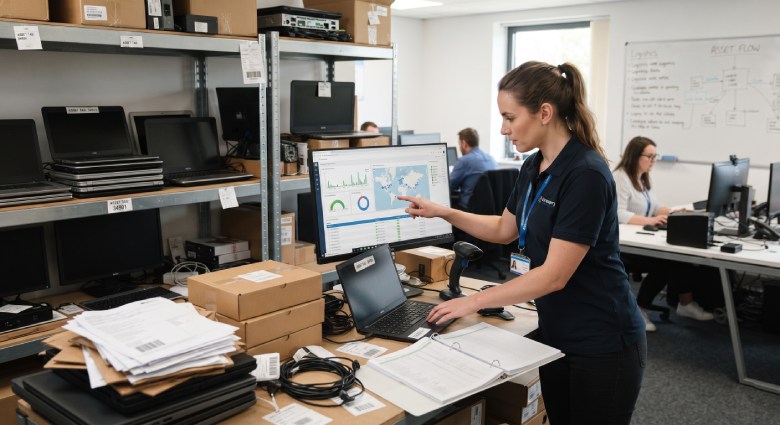
A systems administrator at a mid-sized logistics firm once described her first month on the job as an exercise in archaeology. She inherited a spreadsheet listing 1,400 laptops, a folder of lease agreements that disagreed with it, and a storage closet nobody had opened since the last office move. About a fifth of the machines on the list never checked in, and roughly thirty devices stacked in that closet appeared on no list at all.
Her story is unremarkable, and that is exactly what makes it worth telling. Hardware used to stay where you put it. Desktops lived under desks, servers lived in a room with a badge reader, and an annual walkaround was enough to keep the inventory honest. That world is gone. Laptops now follow people between countries, monitors get shipped to home offices, and a new hire three time zones away may unbox a company machine that IT has never physically touched.
What has not kept pace is the record of what exists. Plenty of organizations can tell you precisely how many software licenses they pay for every month, yet they struggle to say how many laptops they own, who is holding them, or whether the twelve devices bought for a project that wrapped in March are still receiving patches. Hardware visibility has quietly moved from a housekeeping chore to a foundation that security, finance, and IT operations all stand on.
The Quiet Drift From One Office to Everywhere
Distribution happened faster than most asset processes could adapt to it. A procurement cycle that once ended at a loading dock now ends at forty residential addresses, and every one of those shipments creates a record somebody has to capture by hand or not at all. Miss a handful each quarter and the gap compounds, because nothing in the system flags the absence of a device that was never entered.
Onboarding and offboarding make it worse, since those are the moments when hardware changes hands while nobody is watching the ledger. A departing employee returns a laptop to a manager, the manager passes it to whoever needs one next, and two reassignments later the device's official owner has been gone for a year. Multiply that across a few hundred staff and the inventory stops describing the organization you have. It describes one that existed sometime in the past.
What Incomplete Hardware Records Actually Cost
The first cost is plain overbuying. When a request lands and nobody can confirm whether a suitable machine is already sitting in a drawer, the cautious answer is to order another one. Finance watches a capital line climb while utilization stays flat, and no single purchase looks unreasonable enough to challenge.
The second cost is maintenance that lands in the wrong place. Warranty coverage, refresh cycles, and lease returns all run on dates, and dates attached to a device that has been reassigned twice are usually wrong. Teams end up paying out of pocket to repair machines still under warranty, or absorbing penalties on leased equipment that cannot be located before the return window closes.
The third cost is slower and harder to put a number against. Support teams spend their days reconstructing context. A ticket arrives about a failing machine, and before anyone can help, somebody has to establish what the machine is, how old it is, and what has already been tried on it. That detective work happens hundreds of times a year and rarely appears in any budget line.
Where Visibility Becomes a Security Control
Security frameworks have been blunt about this for years. The Center for Internet Security places inventory and control of enterprise assets first among its critical security controls, ahead of configuration management, access control, and everything that follows. The reasoning is hard to argue with, because a device you cannot name is a device you cannot patch, encrypt, or wipe when it goes missing.
The UK National Cyber Security Centre makes a related point in its guidance on managing deployed devices, treating firmware updates, logging, and the retirement of obsolete products as continuing work rather than a deployment milestone. All of that depends on knowing which models are in the field and how many of each, which is precisely the information a stale inventory cannot supply.
Tooling does not rescue you from the gap either. Scanners and vulnerability management tools report on what they can reach, so an unmanaged laptop that never joins the network simply does not appear in the findings. The dashboard looks clean, the risk is real, and the difference between the two is the quality of the asset list underneath.
Building a Record That Stays Accurate
The organizations that get this right stop treating inventory as an annual audit and start treating it as a running log of events. A device gets purchased, assigned, shipped, repaired, reassigned, returned, and retired, and each of those moments is a chance to update one authoritative record. Teams that rely on dedicated it hardware asset management software tend to capture those moments automatically, which matters more than any reporting feature, because a record that updates itself is the only kind that survives a busy quarter.
The practical requirements are modest. Pull from the systems that already know something true: the mobile device management platform, the directory, the procurement queue, the shipping provider. Reconcile the overlaps rather than trusting any one of them. Give one person clear ownership of the record, because shared responsibility for data quality reliably produces none.
Hardware visibility is unglamorous work, and it competes for attention with projects that photograph better in a board deck. It also quietly determines whether half of those projects succeed, since zero trust initiatives, device refresh programs, and security certifications all assume a trustworthy picture of what the company owns.
The administrator in the logistics firm spent her first quarter rebuilding that picture, device by device. She found 60 laptops nobody had claimed, cancelled an order for 40 more, and discovered a batch of machines running an operating system that had stopped receiving updates eleven months earlier. None of those findings were exotic. They had simply been invisible, and invisibility is what makes an ordinary gap expensive.
The distributed environments most companies now run were never designed, they accumulated, and the records describing them accumulated too. Rebuilding one accurate view of the hardware estate is the cheapest correction available, and it gets more expensive every quarter it waits.
Why HR Teams Should Connect Workforce Planning With Talent Development
Weltrade Broker Review: Examining Its Tools and Trading Environment